Ransomware Recovery Services
When ransomware hits, we work fast to get your business running securely again
Virtual Recovery Expertise
High-speed, confidential data retrieval performed remotely, with integrity checks throughout the process.
Client-Centric Frameworks
Tailored security and recovery solutions use robust, multi-layered defense mechanisms to protect uptime, compliance, and data confidentiality.
Proven Technical Expertise
Established expertise for sensitive data safeguarding with years of specialized, confidential service, ensuring complete regulatory compliance and offering proactive defense against modern threats.
What to do after a ransomware attack?
As ransomware threats continue to rise, organizations must adopt a multidisciplinary approach that unites data recovery, IT, and cybersecurity expertise to effectively decrypt and restore compromised systems.
Step 1: Execute the recommended first-response procedures
1. Disconnect all storage media containing backups and isolate servers from the Internet.
2. Verify the integrity of your backups to ensure they can be used for reliable data restoration.
3. Create a secure copy of encrypted data on an external drive or NAS, giving priority to critical systems and virtual machines. Do not reset or reinstall servers, as this can destroy valuable recovery data. These copies are essential for both data recovery and digital forensic analysis.
4. Preserve all evidence related to the attack. Avoid deleting any files and carefully document all indicators of compromise (IOCs) observed.
5. Report the incident promptly to the relevant authorities, such as the police or cybercrime units.
Call us right away to avoid trouble and boost your recovery chances.
Step 2: Choose the Appropriate Recovery Support
Handle it on your own, or let us assist you.
Ransomware:
Recover your paralyzed systems and block the spread of any exfiltrated data.
Stage 1: Data Encryption Initiated
- We analyze the type of ransomware and use known decryptors and public keys, where they exist, to speed up recovery.
- If no decryptor exists, we recover as much as possible directly from the encrypted files and backups.
Stage 2: Data Exfiltration Detected
- Contain and Assess: We quickly isolate affected systems and identify any stolen data to prevent further exfiltration and limit potential damage.
- Recovery and Mitigation: Using advanced forensic analysis, we assist in securing your environment, recovering compromised systems, and implementing measures to prevent future leaks.
Ransomware Recovery Solutions. What Actually Works After an Attack
Modern Ransomware recovery solutions involve far more than decrypting files or restoring a backup. In real-world cyberattacks affecting business-critical servers, virtual machines, databases, and network storage, successful recovery requires a structured, forensic-driven approach. Organizations that expect instant restoration after paying a ransom or applying a decryption tool often face extended downtime, corrupted systems, and incomplete data restoration.
Immediate Ransomware help begins with containment and technical assessment. Once ransomware activity is detected, infected systems must be isolated to prevent further encryption or data exfiltration. Subsequently, security specialists analyze the ransomware variant, its encryption behavior, and the full scope of impact. This analysis is essential—without understanding how the attack operates, recovery attempts can destabilize systems and permanently damage data.
Professional Ransomware Solutions focus on restoring data without relying on attackers. This approach examines encrypted files at the file system and storage level, identifying recoverable data segments and reconstructing damaged file structures. In many incidents, especially when encryption is interrupted or poorly implemented, substantial data can be recovered even when no public decryption tools exist.
Trusted Ransomware Recovery Services also evaluate the viability of backups. While backups are often considered a safety net, many ransomware attacks compromise them before encryption is triggered. We validate backup integrity, scan for dormant malware, and restore data in isolated environments to avoid reinfection. Restoring unverified backups can reintroduce ransomware within hours.
Database-focused attacks present additional complexity. Effective Database Recovery requires more than file restoration—it involves rebuilding transactional consistency and ensuring application usability. In cases of Database Corruption, we analyze indexes, logs, and metadata to safely reconstruct affected databases with as little data loss as possible.
Advanced Database corruption recovery techniques are especially critical for enterprise platforms handling financial, healthcare, or operational data. Ultimately, these processes ensure that recovered databases are accurate, consistent, and safe for production use, not merely accessible.
Specialized Database Recovery Services also support large-scale environments such as virtualized servers, RAID arrays, and NAS systems, where data dependencies are complex and highly interlinked.
File and Storage Recovery
Beyond databases, ransomware often impacts shared storage and individual documents. Professional File Recovery processes rebuild encrypted or partially damaged files while preserving structural integrity and usability.
For organizations running Microsoft environments, SQL Server Recovery demands precise handling of transaction logs, system tables, and database schemas to ensure business applications resume without errors or hidden corruption.
Effective ransomware recovery does not end with data restoration. Systems must undergo post-recovery validation to eliminate persistence mechanisms, backdoors, and vulnerabilities. When executed correctly, this comprehensive approach restores operations securely, minimizes data loss, and prevents repeat attacks—allowing organizations to regain full control after a ransomware incident.
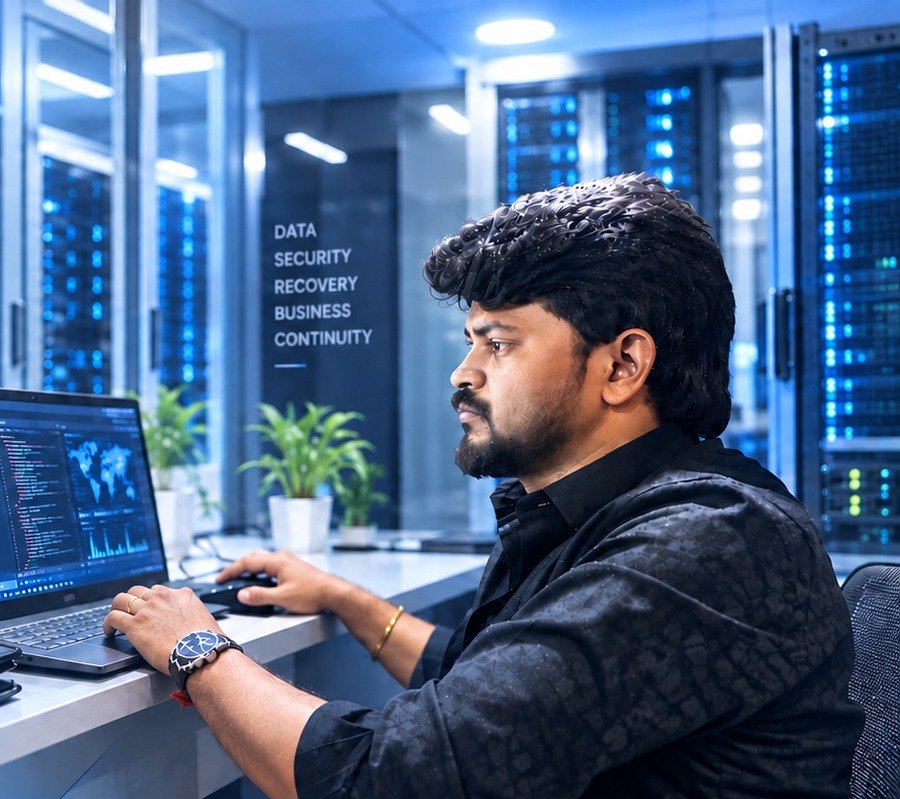
Advanced Ransomware Data Recovery Solutions
Ransomware attacks can lock your files and disrupt your operations within minutes.
We combine advanced tools with deep technical expertise to recover your data safely. We focus on multiple recovery approaches, including decoding encrypted files, reconstructing lost or deleted data, analyzing malware behavior, and repairing compromised systems.
To protect both our methods and your security, we keep the specifics of our tools and processes confidential, ensuring that recovery remains effective and secure.
Ransomware Recovery Services
AS Data Recovery provides specialized ransomware recovery services designed for businesses, IT teams, and organizations dealing with encrypted systems, inaccessible data, or compromised storage environments. These services focus on restoring data safely without relying on ransom payments or unverified decryption tools.
Our ransomware recovery services typically include:
- Ransomware impact assessment
Identification of affected systems, encryption scope, and storage-level damage across servers, endpoints, and connected backups. - Encrypted data recovery
Recovery of files, databases, and virtual disks using controlled, forensic-grade techniques when decryption keys are unavailable or unreliable. - Backup validation and safe restoration
Verification of backup integrity to ensure restored data is clean, usable, and free from dormant malware or encryption triggers. - Enterprise system recovery
Support for RAID arrays, NAS devices, virtual machines, and database platforms where file-level recovery alone is insufficient. - Post-recovery security validation
Ensuring ransomware persistence mechanisms, backdoors, and reinfection vectors are fully removed before systems return to production.
These ransomware recovery services are delivered through remote recovery or our secure lab, depending on data sensitivity, system complexity, and urgency. Each recovery case is handled individually, based on the ransomware variant, infrastructure type, and business continuity requirements.
Rather than offering one-size-fits-all fixes, ransomware recovery services are structured to minimize downtime, protect data integrity, and support safe operational recovery for critical business systems.
Our Recovery Process
Secure File Submission
Files are transmitted using fully encrypted channels.
Comprehensive Assessment
Advanced Data Recovery
Integrity Verification
Key Recovery Metrics
656+
Ransomware recovery cases resolved
4-8h
Typical recovery time for a 100GB database
24/7
Emergency support availability provided
| Ransomware Family | Typical Targets | Encryption Method | Recovery Outlook |
|---|---|---|---|
| LockBit | SQL Server, Oracle, MySQL, virtual disks | Partial encryption of large files | Often partial recovery from the unencrypted parts |
| Akira | Servers, ESXi, Veeam backups | Intermittent encryption | Often partial recovery from the unencrypted parts |
| Phobos / 8Base | Windows servers, databases | Large files encrypted in parts | Often partial recovery of database pages |
| BlackCat/ALPHV | Oracle, PostgreSQL, MySQL | Intermittent encryption | Depends on the mode the attacker used |
| Small files (any family) | Documents, pictures | Usually encrypted completely | Needs backups or shadow copies |
Swift Data Recovery, Your Files, Faster
We offer clear service packages tailored to your deadline and budget.
Emergency (24/7)
- One-on-One Communication
- In-house engineer, never outsourced
- Average Turnaround Time: 1 to 3 Business Days
High-Priority
- Service during business hours.
- 1 Expert Engineer
- Average Turnaround Time: 3 to 7 Business Days
Standard
- Service during business hours.
- 1 Shared Engineer
- Average Turnaround Time: 7 to 14 Business Days
Your Two Options for Ransomware Data Recovery, Remote or In-Lab
We offer flexible and secure recovery options to get your business operational, whether your data is encrypted by ransomware or physically corrupted.
Remote Data Recovery
Remote retrieval is ideal for encrypted or logically damaged data, avoiding the need to physically transport drives. We use a secure SFTP protocol exclusively for transfers. File integrity is checked upon arrival, so you receive identical files. Saves logistical costs, eliminates transit risks and customs issues, and allows your server to stay online.
Laboratory Data Recovery
The majority of complex rescues still take place in our lab. This mode is indispensable for cases where data has been physically deleted, overwritten, or when the storage media itself is damaged (e.g., from physical ransomware attacks that damage the drive). We have far more recovery options and tools with physical access to servers or disks than with downloaded files, maximizing your recovery success.
1- Fill in the form
2- Use Whatsapp for emergencies
Data Recovery FAQs
Frequently asked questions
Get fast, accurate answers to common questions regarding ransomware and data recovery. Find essential information about ransomware attacks, effective decryption, and AS Data Recovery’s expert support. We guide you from prevention to full recovery, showing how to respond swiftly and strengthen your digital defense against future threats.
What is AS Data Recovery's success rate, and is my data recovery guaranteed?
AS Data Recovery has a high success rate for common failures. Our policy is “No Data, No Fee.” You only pay the recovery fee if we successfully recover your specified data. While we cannot guarantee 100% recovery in every scenario, we guarantee you only pay for success.
What is the first thing I should do if my hard drive fails or I realize I've lost data?
How much does data recovery cost, and how long will it take?
Is my recovered data safe and secure during the process?
Can you recover data from devices affected by Ransomware?
Yes, AS Data Recovery specializes in both physical damage recovery and complex logical issues like ransomware encryption. We have advanced tools and techniques to evaluate the integrity of the encrypted files and offer the highest possible chance of successful decryption and full file recovery.
What to Do in the First Hour After an Attack
Firstly, disconnect the infected device from your network immediately. This prevents the ransomware from spreading to other systems. Secondly, do not pay the ransom before speaking with a recovery specialist, since payment does not guarantee your files will be restored.
Preserve Evidence for Investigation
Meanwhile, avoid rebooting the affected machine unless absolutely necessary. Doing so can overwrite forensic evidence needed to identify the ransomware strain. Instead, photograph the ransom note and record any file extensions you notice, then contact us for immediate guidance.
Ultimately, fast and careful action in this first hour often determines whether full recovery is possible. Therefore, treat every minute as valuable and avoid acting alone.
Common Ransomware Recovery Mistakes
Many businesses make the situation worse before help arrives. For instance, some attempt to restore from backups without first confirming the backups themselves are clean, which can reinfect the network. Others assume paying the ransom is the fastest fix, yet studies consistently show a large share of victims never receive a working decryption key even after paying.
Why Timing Matters So Much
Consequently, every hour without action increases the risk that attackers escalate, whether by deploying a second payload or leaking stolen data. Meanwhile, we can often identify the ransomware family within minutes, which shapes the entire recovery strategy that follows. As a result, involving specialists early consistently produces better outcomes than waiting.
A Quick Note on Prevention
Of course, prevention is always better than recovery. Therefore, we also advise clients on hardening their systems afterward, including offline backups, staff training, and network segmentation. In addition, regular patching closes the vulnerabilities attackers rely on most. Ultimately, a strong recovery partner should also help you avoid a repeat incident.
AS IT TECH
Ransomware guides and tools from AS
Buy recovery software at asittech.com →Free downloads
From AS IT TECH — asittech.com, our software and guides site.